Kubernetes | Telemetry collection | Centralized logging
Kubernetes DaemonSet log collection: a practical guide for SecOps
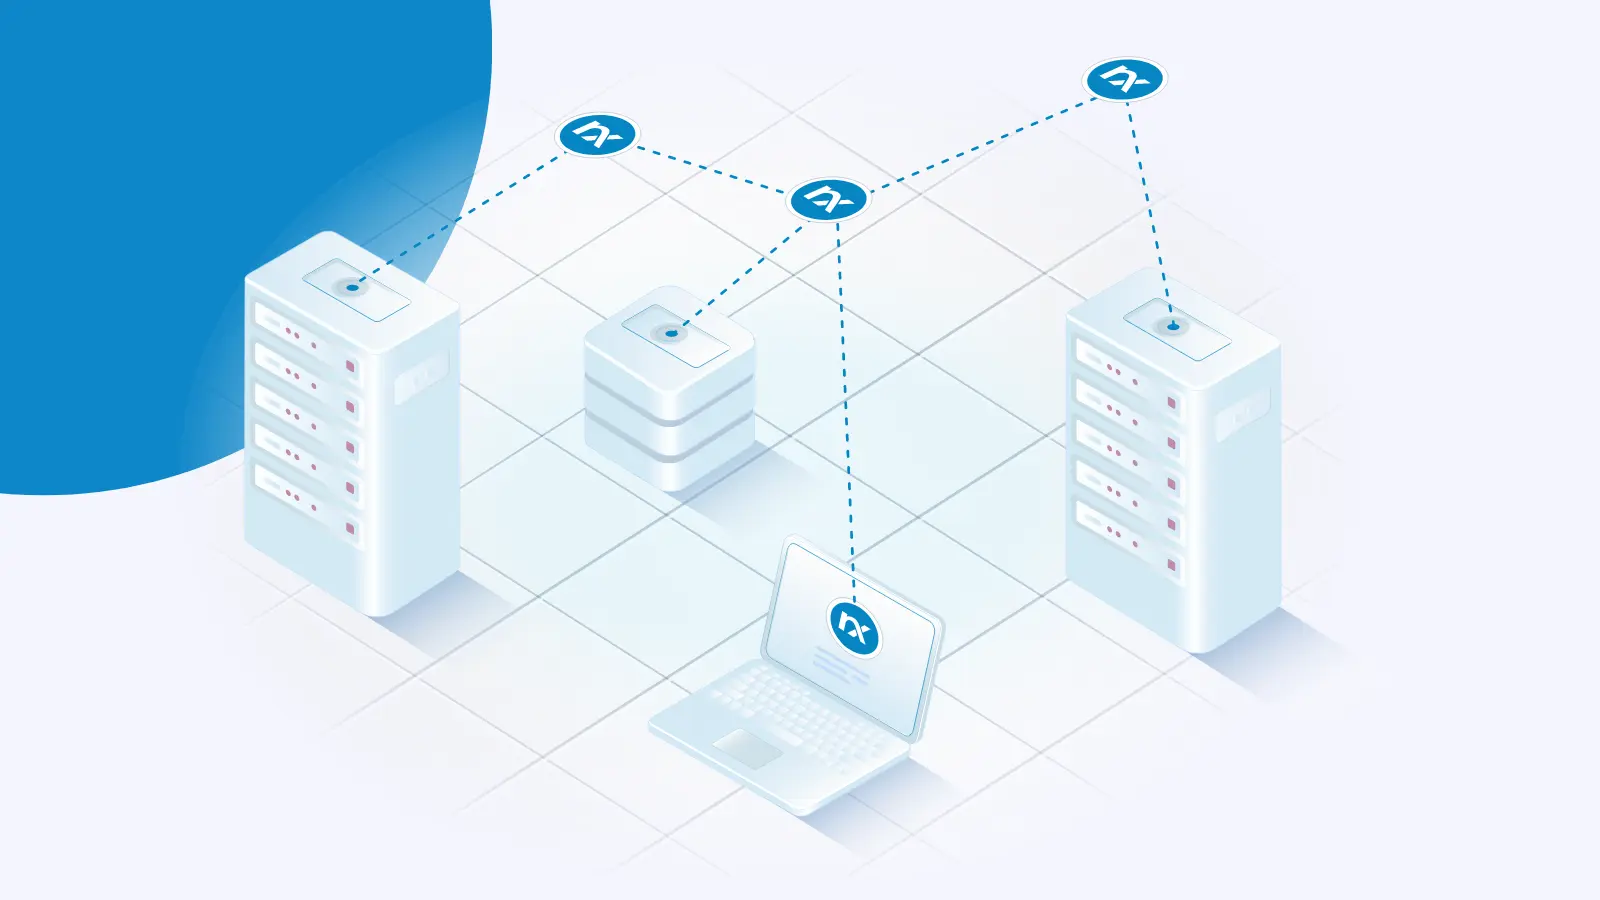
Kubernetes DaemonSet log collection runs one log-collector pod on every node in your cluster. The collector reads all container logs from the node’s /var/log/containers directory through read-only hostPath mounts and forwards them to your SIEM, with no changes to your application pods. When the cluster adds a node, the DaemonSet adds a collector, so coverage scales automatically.
This guide shows you how the pattern works, how Kubernetes writes container logs in 2026, and how to deploy NXLog Agent as a DaemonSet that ships container and audit logs to Microsoft Sentinel or Splunk.