
USE CASE · COLLECTION
Collect telemetry from anywhere
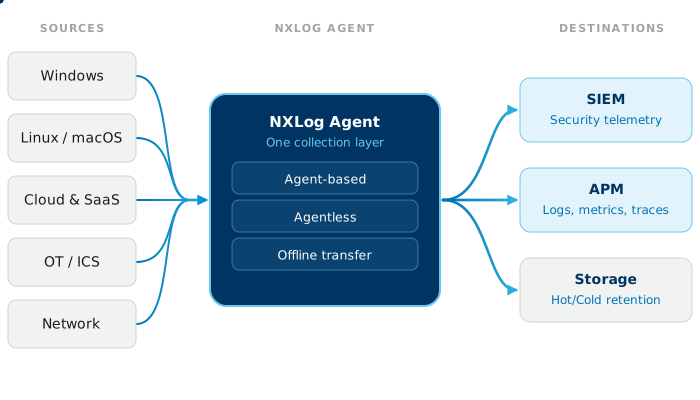
Unify log, metric, and trace collection across your entire estate with agent-based, agentless, and offline modes. One platform that runs where others can’t.
THE CHALLENGE
Real infrastructure is heterogeneous by nature
No one designs a single-OS, single-architecture, single-platform estate from scratch and keeps it that way.

The environment grows organically.
As requirements shift, technology matures, acquisitions land, and integrations multiply — Windows fleets next to Linux servers, macOS endpoints alongside legacy AIX, cloud workloads next to on-prem databases, OT networks beside corporate IT, and air-gapped enclaves where regulation demands them.

A locked-in tool becomes a constraint.
A collection tool locked to one OS family, one deployment model, or one architecture stops being a tool and starts being a constraint. Every new platform becomes a procurement exercise. Every new use case waits on whether the tool can be made to fit.

Visibility fragments across silos.
Teams stand up parallel collection systems to fill the gaps, and visibility fragments across silos that were never supposed to exist.
THE PROBLEM? It isn’t any single environment. It’s that the environment keeps changing — and your collection layer has to change with it, not against it.
THE SOLUTION
Different collection modes for different requirements
NXLog Agent supports agent-based collection where you need control and source-side processing, and agentless collection for devices that can’t run third-party software. There’s even support for offline data transfer.

Deep Windows event collection
Native Windows Event Log API, ETW (Event Tracing for Windows) for kernel and user-mode applications, direct reading of .evt, .evtx, and .etl files, Windows Event Forwarding (WEF) over Kerberos or HTTPS, remote collection over MSRPC, performance counters, and registry monitoring. Built by a team with over a decade of Windows logging experience.

OT, ICS, and SCADA-ready
Collect from industrial control systems and safeguard critical infrastructure without forcing changes on production OT networks. Aggregate events from SCADA, PLCs, and industrial field devices into the same pipeline as your IT telemetry. Data-diode friendly operation with built-in UDP output.

Lightweight enough to run anywhere
Customers cite NXLog Agent’s low CPU and memory footprint as a key reason for choosing it. The agent runs on environments where modern collectors either can’t be installed or consume resources you don’t have to spare — including cell sites, embedded systems, and legacy operating systems.

120+ built-in extensions and pre-built solution packs
Microsoft 365, Okta, Azure Monitor, IIS, OSQuery, OpenTelemetry sources, syslog variants, NetFlow, SNMP traps — collect from the sources you have today, and the ones you’ll add tomorrow.

To build a new robust event collection pipeline, NXLog has been chosen over competitors because of its lightweight, wide support of event sources, integration, and event parsing capabilities.

We really appreciate the versatility of NXLog. It’s ultimately lightweight in regard to CPU/RAM consumption, while still extremely powerful to process a solid event stream flawlessly. Also, as NXLog provides a lot of integration options, it allows us to collect a wide variety of assets’ logs and be flexible with log collection architecture.
INTEGRATIONS
Collect from the sources you have today
|
Windows, Linux, macOS, AIX, Solaris, BSD |
|---|---|
|
Microsoft 365, Azure Monitor, Okta, Salesforce, Amazon S3, Google Cloud |
|
Splunk, Microsoft Sentinel, Google Chronicle, Graylog, QRadar, Securonix, LogPoint |
|
OpenTelemetry collectors and backends, Prometheus, Elastic |
|
SCADA systems, industrial control systems, PLCs and field devices |
|
Syslog (TCP/UDP/TLS), NetFlow, SNMP traps, Check Point OPSEC/LEA, PCAP |


…and many more
RESOURCES
Go deeper
Documentation
Data collection modes
Documentation
Collecting logs from Windows Event Log
GET STARTED TODAY
One collection layer for your whole estate
Start free in your own environment, or talk to us about the platforms you need to collect from — including the ones other tools can’t reach.
Follow us


© Copyright NXLog Ltd.