
A Vector by Datadog alternative built for security teams
Go deeper than the pipeline.
ETW providers, file integrity events, network packets, and Windows hosts with no agent: NXLog Agent collects what a data pipeline can't reach, and NXLog Platform manages every agent from one console — delivered to any SIEM.
Fortune 500 companies trust NXLog


Vector vs. NXLog Platform at a glance
Run NXLog Platform next to Vector
Why teams choose NXLog Platform

Windows collection that has outgrown beta
Vector added its windows_event_log source in v0.55.0, released April 2026, and Datadog's own documentation still labels it beta. NXLog Agent has collected Windows security telemetry for well over a decade: complete EventData and UserData, SIDs resolved to account names, and remote hosts included. When your detections depend on the data, maturity is a feature.

ETW is where Windows hides the good stuff
DNS Server analytical logging, Windows Firewall, and kernel telemetry travel over Event Tracing for Windows, not standard Event Log channels — and Vector has no ETW source. im_etw subscribes to providers directly, so the events land in your SIEM without trace files or conversion scripts.

Inputs a pipeline can't offer
A pipeline processes whatever reaches it. NXLog Agent originates the data: file integrity monitoring, Windows Registry changes, passive packet capture with ICS protocols, ODBC databases, Check Point OPSEC LEA, Linux Audit, and macOS ULS. Your SOC gets sources, not just routing.

Fleet management without a Datadog account
Open-source Vector is configured file by file, host by host. Central management exists — as Datadog Observability Pipelines, a commercial product with Datadog as the control plane. NXLog Platform ships enrollment, configuration, health monitoring, and updates for up to 100,000 agents per node, and support comes from us.

Keep Vector where it earns its place
Vector is a fast routing and aggregation tier, and VRL is a genuinely good transform language. If it serves your clusters well, keep it. Run NXLog Agent across endpoints, servers, and compliance scope — both can feed the same SIEM, and NXLog Agent can even feed Vector.

Independent by design
Vector delivers to many destinations, but its roadmap is set by Datadog. NXLog is an independent vendor with no SIEM to sell you: parsed, normalized events go to Splunk, Microsoft Sentinel, Elastic, Google SecOps, or any syslog, HTTP(S), or Kafka destination — with built-in storage and analytics when you want retention on your own terms.
Questions about coverage? Book a short workshop
Value by Team

SecOps Engineer
Stop writing "no data available" in tickets. ETW providers, file integrity events, and complete Windows event fields give investigations the evidence they usually stall without.

Detection Engineer
Build rules on telemetry, not fragments: DNS analytical logs, Sysmon, PowerShell, Registry changes, and packet-level fields arrive parsed and normalized from the agent.

Compliance & GRC Owner
Cover FIM and audit-trail requirements with the collection layer you already run: file integrity monitoring on Windows and Linux, TLS-encrypted delivery, tamper-proof audit logs, and retention built in.

Security Architect
One agent across six operating systems, deployment on your premises when you need it, and a vendor whose only business is collection. The estate you run today, covered without a redesign.
What you get with NXLog Platform
Every OS in the estate
NXLog Agent runs on Windows, Linux, macOS, BSD, AIX, and Solaris across x86/x64/ARM/PowerPC — and it parses, filters, and routes right where the data is born.
Windows, in full
Event Log with every field and SIDs resolved, ETW providers, Windows Event Collector mode for agentless hosts, Registry monitoring, and Windows performance counters.
Sources the SOC actually needs
File integrity monitoring, passive packet capture with ICS protocol support, ODBC databases, Check Point OPSEC LEA, Linux Audit, and macOS ULS.
Shape data at the source
Parse syslog, JSON, XML, CSV, and key-value pairs; drop the noise before it bills you; enrich events on the endpoint. Custom logic runs in Perl, Python, Ruby, Java, or Go.
A console in the box
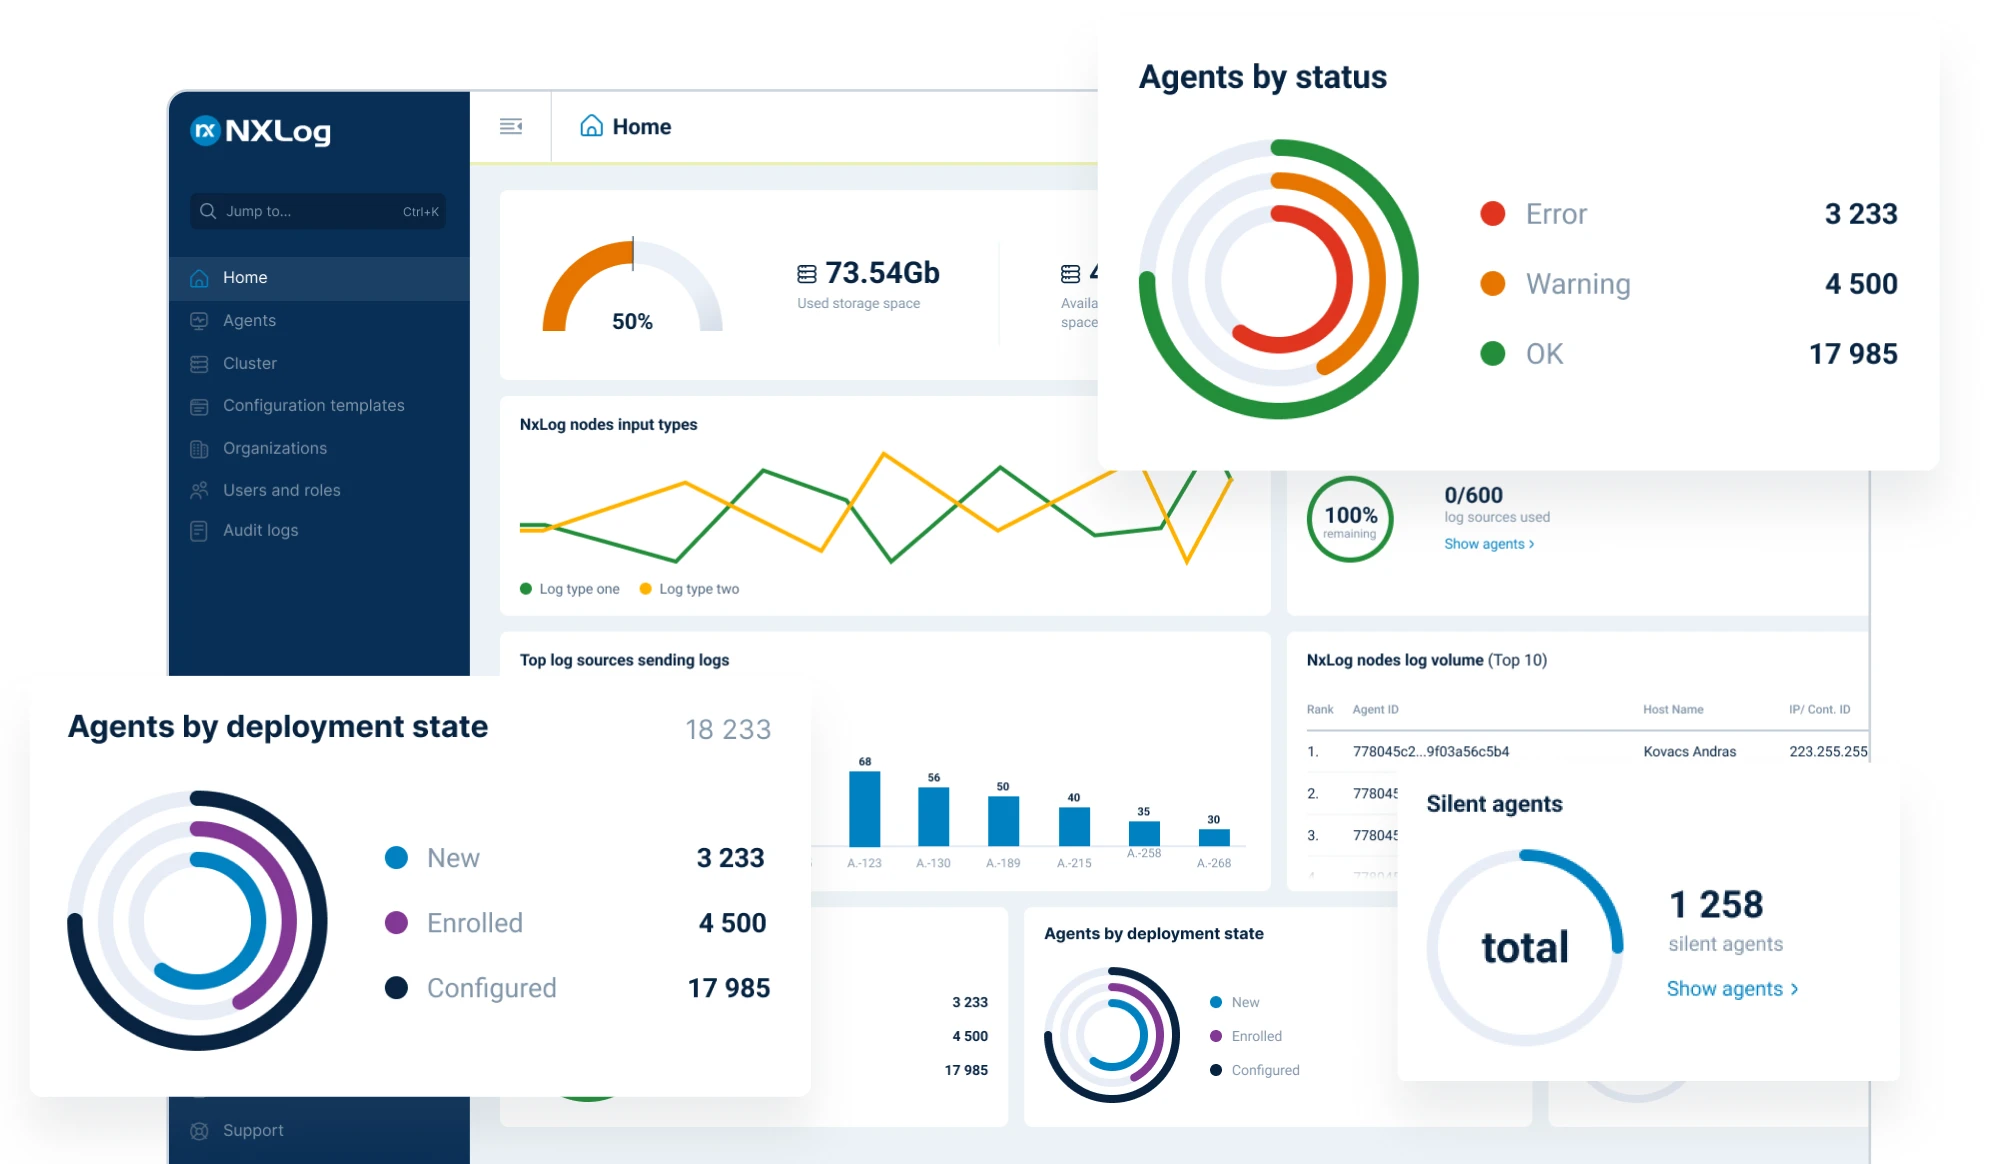
Enroll, configure, monitor, and update agents centrally — with role-based access control, audit trails, and support for up to 100,000 agents per node.
Retention without another contract
High-compression storage, fast search, and dashboards come with the Platform. Pair them with your SIEM, or run them on their own.
Try NXLog Platform for free
FAQs
On the collection side, yes: NXLog Agent covers syslog, file tailing, and Windows Event Log, then adds ETW, file integrity monitoring, packet capture, Windows Event Forwarding, and database sources Vector doesn't offer. If you use Vector as an aggregation tier, NXLog Agent can deliver into it over syslog, TCP, or HTTP — replace the edge first and decide about the middle later.
Yes, and it's the rollout we recommend. Both deliver to the same SIEMs, so you can phase NXLog Agent in host by host with no downtime and compare data quality in your own dashboards.
ETW providers — including DNS Server analytical logging and Windows Firewall — plus remote collection over Windows Event Forwarding, Registry change monitoring, and file integrity events. Vector's windows_event_log source, in beta since v0.55.0, reads local Event Log channels only.
Yes. NXLog integrates with OpenTelemetry pipelines, so choosing NXLog Platform keeps you on open standards. See the NXLog OpenTelemetry solution page for details.
No. Enrollment, configuration, health monitoring, and updates are part of NXLog Platform. With open-source Vector, central management means adopting Datadog Observability Pipelines — a commercial product that runs through Datadog's control plane.
Splunk, Microsoft Sentinel, Elastic, Google SecOps, OpenSearch, and any syslog, HTTP(S), or Kafka destination. NXLog Platform also includes its own storage and analytics if you want retention outside the SIEM.
Vector is a trademark of Datadog, Inc. Product information is based on publicly available documentation as of July 2026.
Follow us


© Copyright NXLog Ltd.