
A ManageEngine EventLog Analyzer alternative | NXLog
Collect deeper. Route anywhere.
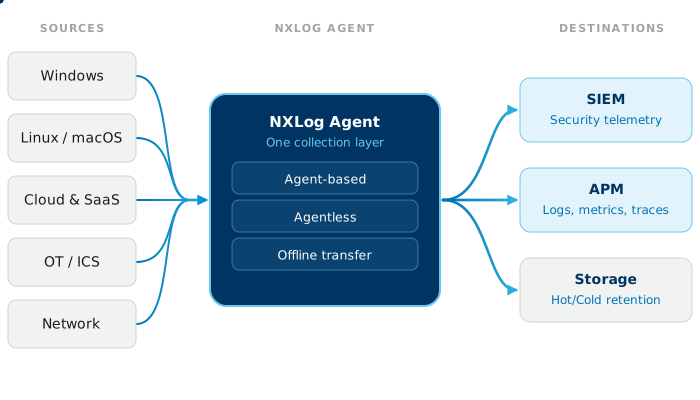
NXLog Platform captures the Windows telemetry WMI polling doesn't see — ETW traces, Windows Event Forwarding streams, Registry changes, file integrity events — along with Linux, macOS, and the AIX and Solaris estates most collectors dropped years ago. It filters at the source and delivers to any SIEM you run, or stores and searches the data itself. One collection layer, no second console.
Fortune 500 companies trust NXLog


ManageEngine EventLog Analyzer vs. NXLog Platform at a glance
Walk through NXLog Platform at your own pace — agent enrollment, pipeline, storage, and search included
Why security teams pick NXLog Platform over EventLog Analyzer

Feed the SIEM you already trust
EventLog Analyzer collects into EventLog Analyzer: its reports, alerts, and search assume it's the destination. NXLog Platform collects once and delivers wherever your detections run — Microsoft Sentinel, Splunk, IBM QRadar, Google SecOps, an OpenTelemetry endpoint, or NXLog's own storage and search. Your SIEM keeps its context; you skip the second console.

Windows telemetry beyond the Event Log
WMI polling reads event logs. NXLog Agent also captures ETW traces, Windows Event Forwarding streams, Registry changes, file integrity events, and Microsoft DNS Server logs — the channels investigations turn on.

Agentless, minus the stored credentials
EventLog Analyzer's default agentless mode polls hosts over WMI, which means DCOM ports open across the estate and collection credentials held on one server. NXLog does agentless through Windows Event Forwarding: hosts push events to a collector, with no collection account to provision or protect.

No central parsing bottleneck
ManageEngine's own best practices guide rates a standalone node at about 2,000 events per second for Windows event logs and 20,000 for syslog; past that, you're designing a distributed deployment. NXLog Agent parses and filters on each endpoint, so throughput grows with the fleet instead of queuing at one server.

Every OS from one console — including the old ones
EventLog Analyzer agents cover Windows and Linux; everything else arrives as syslog. NXLog Agent runs natively on Windows, Linux, macOS, FreeBSD, AIX, and Solaris, with legacy modules for Windows XP, 2000, and 2003 — every agent enrolled, configured, and updated from NXLog Platform.

Send less, keep the signal
NXLog Agent drops, rewrites, and converts events at the source, so only data worth keeping leaves the host. Whatever sits downstream — EventLog Analyzer included — indexes less noise.
Start your free 30-day trial
Value by Team

SOC engineers
Your investigations live in your SIEM, not in a side console. NXLog lands every signal where your detections already run — with the ETW and WEF depth that WMI polling misses.

Compliance owners
Raw logs, unmodified, on storage you control, with HMAC integrity checking on the pipeline. Retention follows your policy, and collection still reaches the legacy systems your audit scope includes.

IT operations
Thousands of agents are a fleet, not a folder of relay hosts. Enroll, configure, monitor, and update from one console — across Windows, Linux, macOS, and the AIX and Solaris boxes everyone else dropped.

MSSPs
One pipeline per client, delivered to whichever SIEM they run. Per-source pricing you can quote in advance, every feature on every plan, and volume discounts past 100 sources.
What you get with NXLog Platform
Native Windows security collection
Windows Event Log through the modern API, Event Tracing for Windows for channels the Event Log doesn't carry, agentless collection as a Windows Event Collector for WEF clients, Registry monitoring, file integrity monitoring, performance counters, and Microsoft DNS Server log parsing. Legacy modules cover Windows XP, 2000, and 2003 where they still run.
Route to any SIEM — or run without one
NXLog Agent forwards to Microsoft Sentinel, Splunk, IBM QRadar, Google SecOps, Securonix, and ArcSight, and speaks OTLP over HTTP(S) and gRPC to OpenTelemetry backends. Prefer to keep some data out of the SIEM bill? NXLog Platform stores logs on your infrastructure and gives you search on top.
Manage agents like a fleet
Enroll agents, distribute configuration centrally, watch health, and roll out updates remotely from NXLog Platform. Solution packs give you working pipelines for common routes — Windows to Google Chronicle, syslog to an OpenTelemetry backend, Okta to Google SecOps — so day one starts from a template, not a blank config.
Process at the source
Filter events, rewrite fields, and convert between formats — syslog, JSON, XML, CSV, CEF, LEEF, GELF — before data leaves the host. Buffer to disk through outages, compress and encrypt in transit, and de-duplicate repeating messages. Whatever you run downstream receives structured events, not raw noise.
Source-based licensing, explained
A source is a system, device, or application NXLog collects from — a server, a firewall, a container cluster. You pay per source, flat: ETW, file integrity monitoring, Registry monitoring, DNS parsing, and every output are included on every plan. No add-on SKUs, no per-type price list. The Free plan covers up to 10 sources with the full feature set.
Keep EventLog Analyzer in the loop — if you want
You don't have to rip anything out on day one. EventLog Analyzer includes a built-in syslog server (default listener ports 513 and 514), and NXLog Agent forwards standard syslog over UDP, TCP, or TLS. Put NXLog in front: reach macOS, AIX, ETW, and isolated segments WMI can't, trim noise before it counts against the node's throughput, and keep existing reports running. It's plain syslog on both ends — no connector to buy, no new lock-in. Repointing outputs later is a configuration change, not a re-instrumentation project.
Try NXLog Platform for free
FAQs
For log collection, agent management, storage, and search — yes, with deeper Windows telemetry and delivery to any backend you choose. EventLog Analyzer also bundles analytics: correlation rules, threat intelligence feeds, MITRE ATT&CK mapping, and predefined compliance reports. NXLog Platform doesn't ship detection content. It feeds whichever analytics layer you trust — your SIEM, or EventLog Analyzer itself — or stores and searches the data on its own. If those bundled analytics are why you run it, see the next two answers.
They're real. EventLog Analyzer ships predefined reports for PCI DSS, HIPAA, FISMA, SOX, GLBA, ISO 27001, and the GDPR, and if those templates carry your audit today, we won't pretend otherwise. NXLog Platform approaches compliance from the collection side: coverage that includes legacy systems, unmodified raw logs with HMAC integrity checking, and retention on storage you control — delivered to the reporting tool your auditors already accept. Audits are won on complete collection and provable retention; the report layer can be whatever your assessors already use.
Both license per source — neither meters gigabytes. The structure differs. EventLog Analyzer prices by device type — Windows workstations, Windows servers, syslog devices — with add-ons such as application auditing, Linux file auditing, and Advanced Threat Analytics; as of August 2026, ManageEngine lists the Premium edition from $595 per year, Distributed from $2,495, an endpoints package at $245 per 100 endpoints, and a Free edition covering 5 log sources. NXLog Platform Premium is one flat rate per source with every feature included: $12.12 per source per month at 11 sources, falling to $5.58 at 100, with volume discounts above that — and the Free plan covers 10 sources. At small counts the entry prices are close; the difference is what's included and how the bill behaves as you add device types and capabilities.
Yes. EventLog Analyzer's built-in syslog server listens on ports 513 and 514 by default, and NXLog Agent forwards standard syslog over UDP, TCP, or TLS. Its custom log parser can extract fields from what NXLog sends. Teams run this way to reach sources WMI can't — macOS, AIX, ETW channels, isolated segments — and to trim noise before it reaches the server. Plain syslog on both ends: nothing extra to buy, and no new lock-in.
Log360 is ManageEngine's SIEM suite; EventLog Analyzer is its log management component, sold alongside Active Directory auditing, UEBA, and SOAR modules. If you're evaluating Log360, the question isn't NXLog versus Log360 — it's whether your collection layer should belong to your SIEM vendor. NXLog Platform stays vendor-neutral: it can feed Log360 today and Microsoft Sentinel, Splunk, or Google SecOps tomorrow, without re-instrumenting the estate.
Windows, Linux, and macOS, plus FreeBSD, IBM AIX, and Oracle Solaris — on x86, ARM, IBM Power, and SPARC hardware. On macOS that includes the Unified Logging System and Endpoint Security events, not just syslog. Legacy input modules cover Windows XP, 2000, and 2003. If part of your estate predates your SIEM, NXLog can still read it.
ManageEngine and EventLog Analyzer are trademarks of Zoho Corporation Pvt. Ltd. All other product names, logos, and brands are the property of their respective owners. NXLog is not affiliated with, endorsed by, or sponsored by Zoho Corporation. Comparison statements reflect publicly available documentation as of August 2026.
Follow us


© Copyright NXLog Ltd.