
A Logmanager alternative built for security teams
Every OS in. Any SIEM out.
One appliance shouldn't decide what you can see. NXLog Agent collects security telemetry from Windows to AIX and delivers it to Splunk, Microsoft Sentinel, Google SecOps, OpenSearch, or Elastic — several at once — and NXLog Platform retains it without a per-GB meter.
Fortune 500 companies trust NXLog


Logmanager vs. NXLog Platform at a glance
Run NXLog Agent alongside Logmanager and compare coverage
Why teams choose NXLog Platform

Deliver past the box
Logmanager's route to a third-party SIEM is a syslog output over TCP, and its documentation notes that messages are lost when the remote side stops responding. NXLog Agent delivers natively to Splunk, Microsoft Sentinel, Google SecOps, OpenSearch, and Elastic — several destinations in parallel, with disk buffering when a link goes down.

Agents where Logmanager has none
The Logmanager agent runs on Windows only; Linux and macOS hosts push syslog you set up and maintain per machine. NXLog Agent installs as a supported package on Windows, Linux, macOS, FreeBSD, AIX, and Solaris — one collection layer, enrolled and managed the same way everywhere.

Windows depth past Event Log channels
Logmanager's agent bundles Elastic Filebeat and Winlogbeat, so its documented scope is Event Log channels and flat files. NXLog Agent adds ETW providers, file integrity and Registry monitoring, performance counters, and a Windows Event Forwarding collector role — which can run on a Linux host.

Fleet changes without the hourly wait
Logmanager's Windows agents pull configuration from the appliance on a one-hour heartbeat. NXLog Platform handles enrollment, configuration, monitoring, and updates fleet-wide — up to 100,000 agents per node, with RBAC and audit trails over who changed what.

Keep Logmanager where it fits
A mostly-Windows estate, syslog-speaking network gear, one admin? Logmanager covers that well — keep it. NXLog Agent can feed the same box over syslog while adding what it lacks: agents beyond Windows, deeper endpoint telemetry, and delivery to the SIEM on your roadmap.

Shape events before they ship
Logmanager drops events at the agent with Beats filters and parses on the appliance, after everything crosses the wire. NXLog Agent parses, rewrites, enriches, and masks at the source — extensible in Perl, Python, Ruby, Java, or Go — so what lands downstream is already clean.
Planning a rollout? Book a short workshop
Value by Team

SecOps Engineer
Feed Microsoft Sentinel, keep Logmanager's dashboards alive, and store an archive copy — all from the same agents, while the hand-edited rsyslog configs on your Linux fleet finally retire.

Detection Engineer
Detection logic is only as good as its inputs. Get full-fidelity Event Log fields, ETW providers, and Registry and file integrity changes, normalized by the agent — not reconstructed from syslog strings.

Compliance & GRC Owner
Retention set by policy, not by appliance capacity: high-compression storage, encrypted transport, file integrity events from the collection agent itself, and an audit trail on every fleet change.

Security Architect
One collection layer that can feed Logmanager today, your next SIEM tomorrow, and both during the switch — deployed from Windows to AIX, cloud or on-prem, so the next SIEM decision doesn't force the next agent rollout.
What you get with NXLog Platform
Agents from Windows to AIX
One agent, from desktop Windows to AIX in the datacenter — supported packages on six operating systems and four processor families, with the same configuration language on all of them.
The full Windows security surface
Every Event Log channel and field with XPath filtering, ETW providers, Registry and file integrity monitoring, performance counters, and a collector role for Windows Event Forwarding — supported modules in one agent.
Sources past the syslog stream
Rows from databases over ODBC, Linux Audit rules, the macOS unified log and Endpoint Security, packet capture with ICS protocol support, Check Point OPSEC LEA, and Microsoft 365 — collected without side tooling.
Parse first, ship second
Events get parsed, filtered, and masked on the host that produced them — syslog, JSON, XML, CSV, and key-value pairs — with custom logic in Perl, Python, Ruby, Java, or Go when the built-ins aren't enough.
A fleet console built for scale
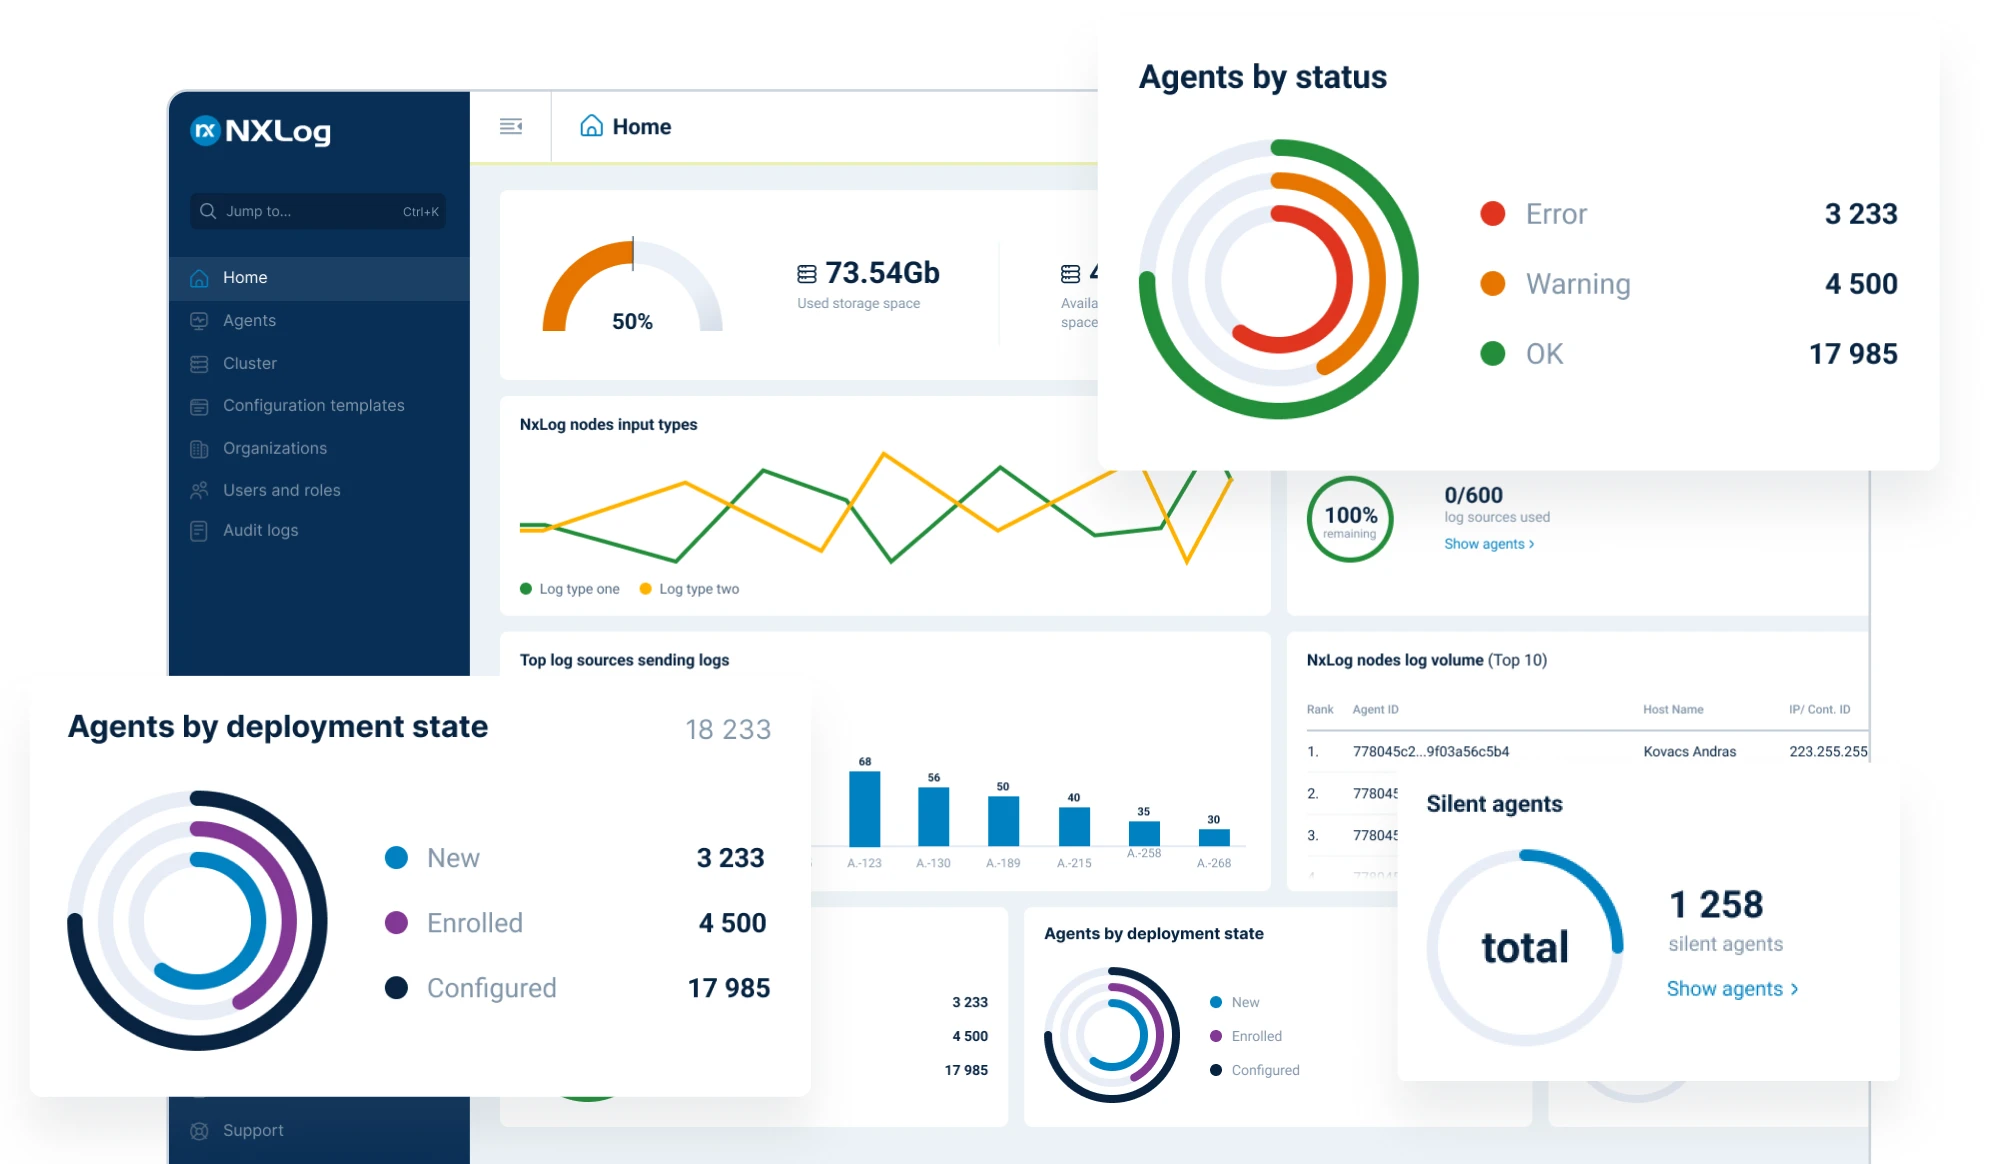
Enrollment, configuration, updates, and health for the whole estate in one console — gated by RBAC, recorded in audit trails, and rated for up to 100,000 agents per node.
Retention without a meter
Storage, search, and dashboards are part of the platform, with high compression keeping the footprint down. Hold data as long as policy demands, keep a copy outside the SIEM, or skip the SIEM entirely — the per-source price doesn't move.
Try NXLog Platform for free
FAQs
For collection, storage, search, and dashboards — yes, and each gets wider: agents on six operating systems instead of one, native SIEM delivery instead of a syslog output, and retention priced by source. Logmanager's correlation alerts don't transfer as-is; most teams rebuild detection in the SIEM that NXLog feeds, where those rules live long term.
Yes. Logmanager ingests syslog, and NXLog Agent speaks it — so you can upgrade the collection layer first and keep the box as your store. The same agents can mirror a second stream to Microsoft Sentinel, Splunk, or OpenSearch while you evaluate.
The Logmanager agent bundles Elastic Filebeat and Winlogbeat, which cover Windows Event Log channels and flat files. NXLog Agent adds ETW providers, file integrity and Registry monitoring, packet capture with ICS protocol support, database collection over ODBC, Linux Audit, and the macOS unified log — and it runs as a managed agent on Linux and macOS, which Logmanager's doesn't.
Yes. Deploy NXLog Platform on your own infrastructure or use the cloud-hosted service — agents, delivery, and storage work the same either way, so the choice is about where you want the console, not what you give up.
Logmanager charges for the data you store; by its own documentation, once the storage limit is exceeded the oldest data is overwritten to make room. NXLog Platform licenses by source: verbose applications, incident spikes, and longer retention don't change the bill, and there are no EPS or volume caps.
Microsoft Sentinel, Splunk, Google SecOps, Elastic, and OpenSearch natively; IBM QRadar and ArcSight through LEEF and CEF; plus syslog, HTTP(S), Kafka, and OpenTelemetry for everything else — several routes at once when you want a SIEM feed and an archive. Retention inside NXLog Platform covers the copy you keep.
Logmanager is a trademark of its respective owner. Product information is based on publicly available documentation as of July 2026.
Follow us


© Copyright NXLog Ltd.