
A Loggly alternative
Your logs. Your infrastructure. No daily caps.
Collect security telemetry from Windows, Linux, macOS, and network devices, process it at the source, and keep it as long as your auditors require — with one cross-platform agent and no per-GB pricing.
Fortune 500 companies trust NXLog


Loggly vs. NXLog Platform at a glance
Try NXLog Platform alongside Loggly
Why teams choose NXLog Platform

Keep every log during an incident
Security incidents create log spikes — and Loggly plans cap daily volume, with data above the cap left unindexed. NXLog Platform has no volume or EPS limits, and agent-side buffering holds events through network outages. Your investigation never starts with missing data.

Loggly's own guides use NXLog on Windows
Loggly is agentless, so its documentation points Windows users to NXLog for Event Log collection. If you run Loggly on Windows, you likely run our agent already. NXLog Platform gives that agent a pipeline, storage, analytics, and fleet management to report to.

Retention that satisfies auditors
Loggly retention tops out at 90 days, and older data moves to S3 archives you can't search from Loggly. With NXLog Platform, you set the retention period on storage you control — 12 months for PCI DSS, longer if your policy requires it.

Your data stays where you put it
NXLog Platform runs on your infrastructure: on-premises, in your cloud account, or in air-gapped networks. Sensitive security telemetry stays searchable without leaving your environment.

Log more without paying more
NXLog licenses by source, not volume. Verbose sources like Sysmon, DNS, and ETW cost the same as quiet ones — so no one is tempted to switch off the telemetry your detections depend on.
Collect everything. Cap nothing.
Value by Team

SOC Analyst / Detection Engineer
Complete Windows, macOS, and Linux telemetry with filtering and enrichment at the source. Less noise in, better detections out.

Security Engineer
One agent across every OS and architecture, managed from one console — up to 100,000 agents per node.

Compliance / GRC
Retention you control, file integrity monitoring, and tamper-evident audit trails. Evidence your assessors can work with.

CISO / Security Manager
Source-based pricing keeps the budget flat as data grows. Vendor-agnostic routing means no lock-in.
What you get with NXLog Platform
One agent, every OS
One cross-platform agent (Windows, Linux, macOS, BSD, AIX, Solaris; x86/x64/ARM/PowerPC) for endpoint and network collection, processing, and routing.
Security-grade collection
Native Windows Event Log and ETW, file integrity monitoring, Windows Registry monitoring, macOS Endpoint Security, Linux Audit, DNS, network devices — 120+ built-in integrations.
Processing at the source
Parse (JSON, CSV, XML, key-value, syslog, Grok), filter, enrich, and mask PII before data crosses the network.
Built-in storage and analytics
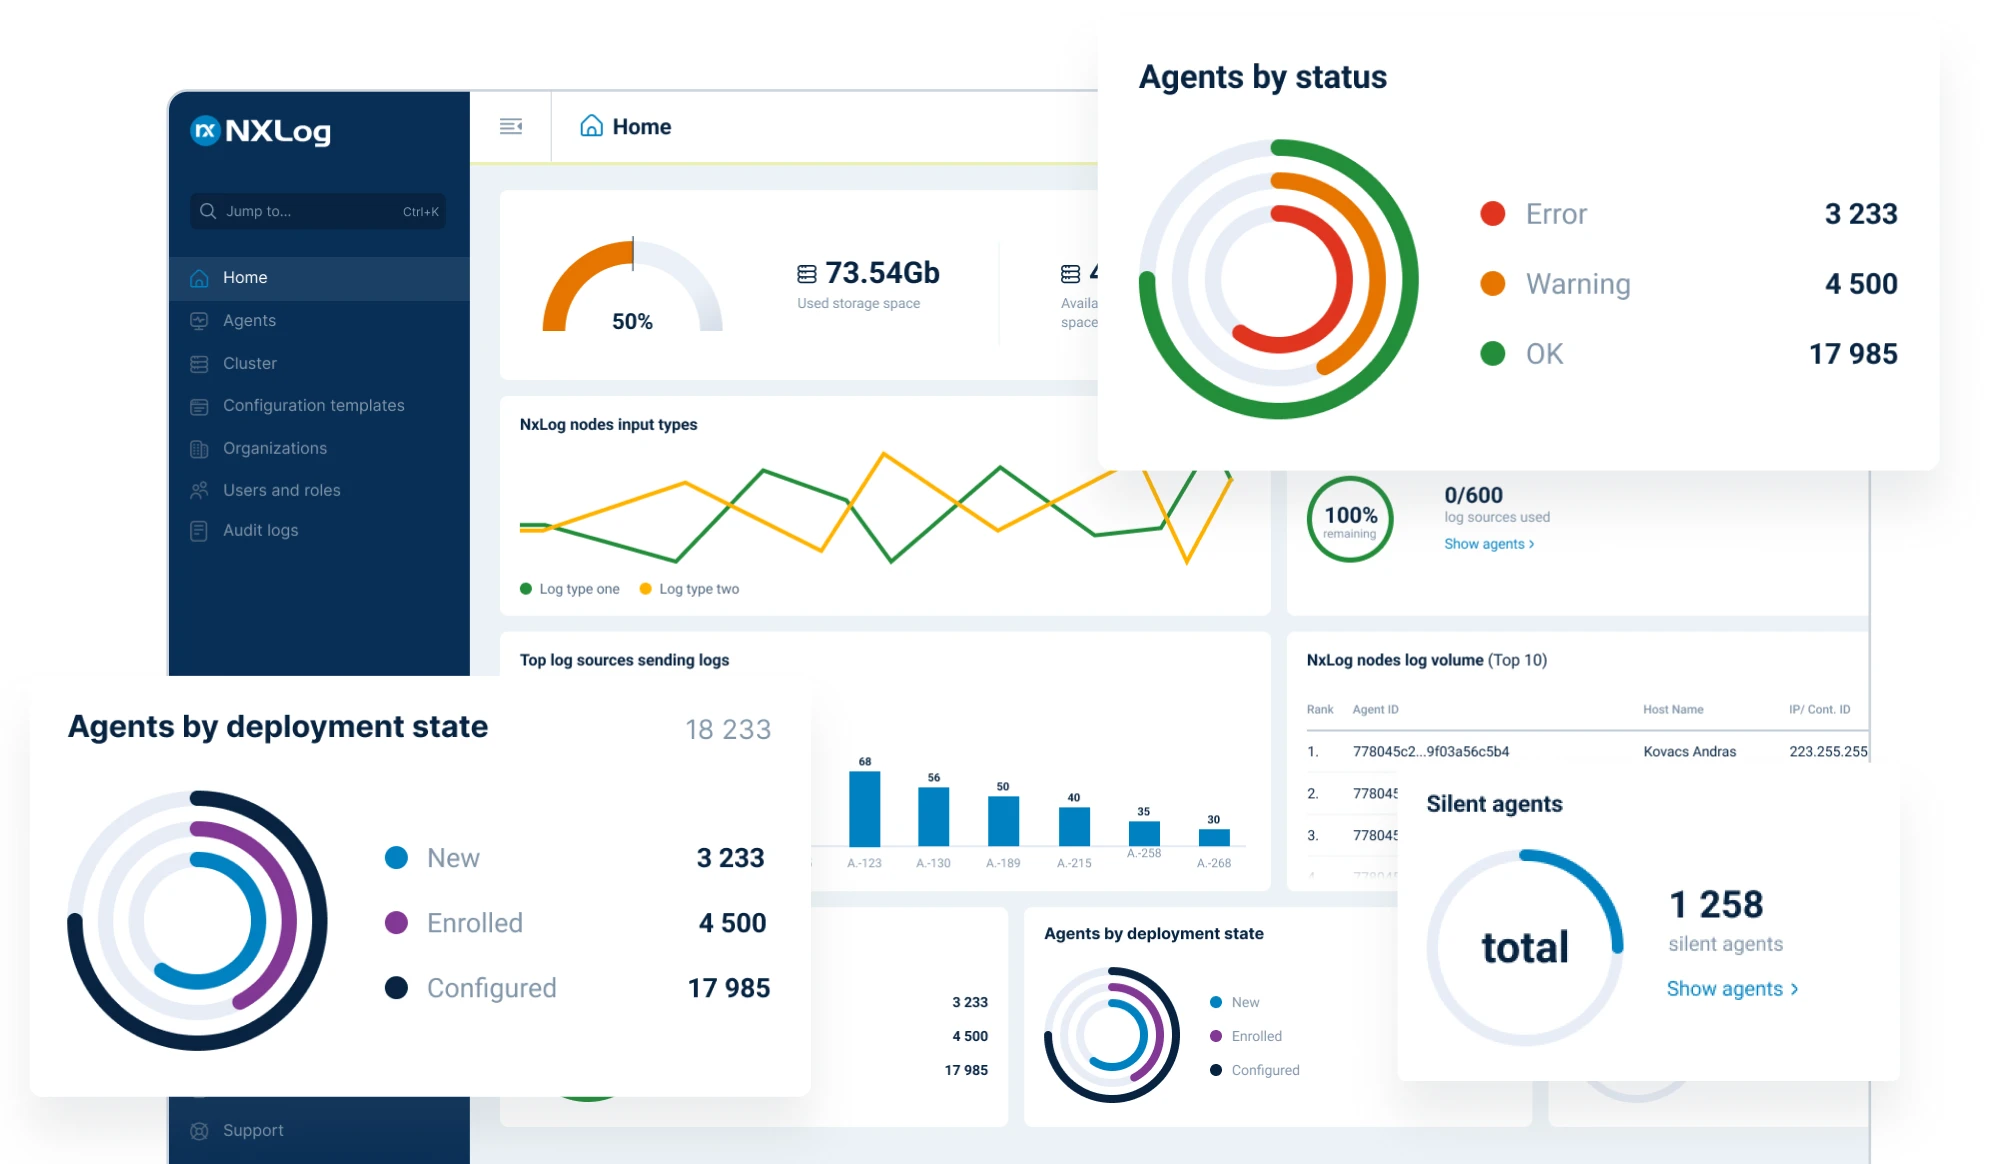
High-compression retention, fast search, and dashboards. Use alongside or without a third-party SIEM.
Fleet management and security
TLS in transit, RBAC, audit logs, and centralized configuration for up to 100,000 agents per node.
Try NXLog Platform for free
FAQs
For log collection, centralization, search, dashboards, and alerting — yes, and it adds processing at the source, retention you control, and fleet management. Applications that send logs to Loggly over syslog or HTTP can send them to NXLog Platform the same way.
Yes. NXLog is vendor-agnostic, so the agent can send the same stream to Loggly and NXLog Platform in parallel until you're ready to switch.
Nothing changes. NXLog Platform has no per-GB fees, volume caps, or EPS limits, and buffering carries events through outages.
Yes. You set the retention period on storage you control, so PCI DSS and similar mandates don't depend on a plan tier.
No. Enroll them in NXLog Platform, manage them centrally, and re-route the output when it suits you.
Wherever you deploy NXLog Platform — your data center, your cloud account, or an air-gapped network.
Loggly is a trademark of SolarWinds Worldwide, LLC. Product information is based on publicly available documentation as of July 2026.
Follow us


© Copyright NXLog Ltd.