
A biotech S&P 100 company unified log collection and stayed on its existing SIEM tier
With NXLog, a global biotech company brought logs from thousands of Windows endpoints, Linux systems, and network devices into one pipeline, filtered them before they reached IBM QRadar, and built the audit trail its HIPAA, FDA, and GDPR obligations require.

Business Demand
Meet HIPAA, FDA, and GDPR obligations across international operations while improving security posture.
Key Challenges
Collect from thousands of Windows endpoints, Linux systems, Cisco network devices, and multi-vendor firewalls, then feed one SIEM in a format it accepts.
Results
One unified pipeline, near real-time threat detection, an audit-ready trail, and no rise in SIEM licensing costs.
The investment into building a security observability pipeline with NXLog not only fortified our existing IT infrastructure but also made room for us to grow securely. As we continue to innovate in biotech, we can rely on NXLog Platform to scale with us, making sure security and compliance risks are managed properly.
— Chief Information Security Officer, S&P100 Biotech Company

The Challenge
Our customer is a global biotech company that handles some of the most tightly regulated data there is: proprietary research output on one side, personal health information on the other. HIPAA governs how it protects patient health information. FDA regulations require meticulous record-keeping across research and development. GDPR governs personal data across its international operations. Failing any of them carries legal penalties, and a leak would cost the company something harder to repair than a fine.
Log management sits underneath all three. Continual incident detection and response depends on it, and so does the evidence an auditor asks for. The problem was the estate underneath that: thousands of Microsoft endpoints (Windows 10 and 11 workstations, Windows Server 2016 and 2019), Linux systems spanning Red Hat Enterprise Linux 8 and 9, CentOS, and Amazon Linux, Cisco routers and switches, and firewall appliances from several different vendors.
Every one of those generates logs in a different format, and reaching them takes different protocols. Collecting centrally from that mix is difficult on its own. The customer also had a destination to satisfy: IBM QRadar, its existing SIEM. General-purpose SIEM platforms concentrate on correlation and analytics, and their native collection tooling is built for the common cases rather than the long tail of a mixed estate — so the security team needed a collection layer of its own, one that could hand QRadar compliance-ready data in a format it already understood. On top of that, R&D expansion was pushing log volume up sharply, and moving all of it across the network would have cost bandwidth, storage, SIEM performance, and budget.

The Solution
After evaluating several vendors, the customer chose NXLog Platform. The collection architecture was designed first, then deployment began.
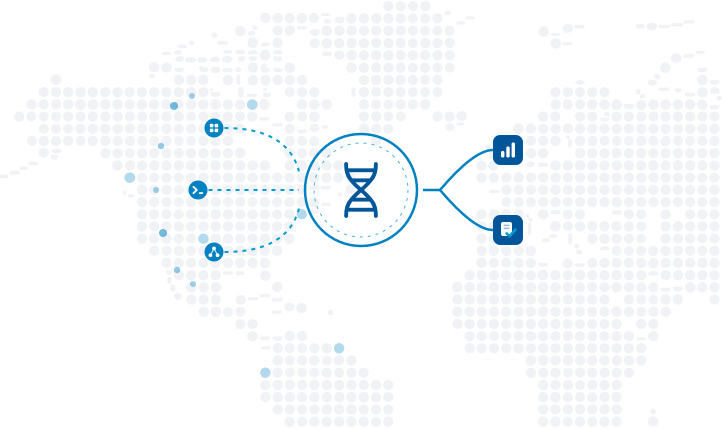
One agent covered all three source types. On Windows, the im_msvistalog module collects Windows Event Log records from workstations and servers — security events, system errors, application issues, and more. On Linux, im_file reads the files the compliance program depends on, including /var/log/messages, /var/log/secure, and application-specific logs. For network devices, im_udp and im_tcp take syslog messages from Cisco routers and firewalls over both UDP and TCP.
A single management interface sits above all of it, covering the thousands of agents and collectors installed across the environment, so configuration is one job rather than one job per platform.
What happens to the data in transit is what protected the SIEM. Agents parse unstructured messages using regular expressions and built-in parsers, which lets the customer filter at the source and forward only what the SOC can act on. Fields are then normalized so the same event looks the same whatever produced it, and converted into JSON, XML, or CSV as needed. Logs go to QRadar directly, with no intermediate hop, and custom parsing and mapping rules match the format QRadar expects.
Compressed batch transport handled the bandwidth problem. Sending events in compressed batches rather than one at a time cut the volume crossing the network and took pressure off constrained links.
Why it Worked

Native collection for Windows, Linux, and network devices

Source-side filtering before data reaches the SIEM

Compressed batch transport over constrained links

Direct QRadar delivery with custom mapping rules
Results
Since deploying NXLog Platform, the customer's security team works from one centralized set of log data instead of chasing it across platforms. Alerts on that data support close to real-time threat detection, and immediate access to the full record has shortened both investigation and remediation — incident response improved as a direct result.
Compliance got easier to demonstrate rather than easier to claim. Every log the programs require is collected, stored, retrievable on request, and disposed of on schedule, which is what a transparent audit trail actually means when an auditor asks for it.
The cost side worked out too. Because pre-filtering cut the volume of data collected, the customer stayed on its existing SIEM licensing tier instead of moving up one — the growth in R&D logging did not turn into a bigger SIEM bill.
And because everything now lands in one place, reporting is unified across teams and departments that previously each had their own view.

Near real-time threat detection
Alerts on centralized log data help the team act sooner
Audit-ready evidence
Logs collected, stored, retrievable, and disposed of on schedule
No SIEM tier increase
Source-side filtering kept the customer on its existing licensing tier
Unified reporting
One centralized set of log data across teams and departments
About the customer
The customer is a global biotech company in the S&P 100, with a long history of discovering, developing, and delivering medicines. Its work spans proprietary research and personal health information across international operations, which places it under HIPAA, FDA, and GDPR at the same time.
Follow us


© Copyright NXLog Ltd.