
A global energy company gained real-time DNS visibility without flooding its SIEM
With NXLog Platform, the company captured high-value Windows DNS Analytical events at the source, dropped low-value queries before ingestion, and delivered normalized, encrypted telemetry into Palo Alto Networks Cortex XSIAM.

Business Demand
Strengthen security posture, meet regulatory compliance obligations, and reduce SIEM costs.
Key Challenges
Capture and analyze Windows DNS Analytical logs across heterogeneous infrastructure — Windows, Linux, and network devices — and feed one integration into Palo Alto Networks Cortex XSIAM.
Results
A unified, real-time view of DNS activity, lower SIEM ingestion, auditable encrypted logs, and threat detection on DNS data that was previously unusable.

The Challenge
A major North American energy company set out to strengthen its security posture and regulatory compliance while reducing SIEM costs. Responsible for critical pipeline systems and power facilities, it needed to capture and analyze Windows DNS telemetry across a wide network of servers as efficiently as possible.
The company's Windows DNS estate was a key telemetry source for identifying suspicious or anomalous network behavior. But DNS Analytical logs are complex and they arrive in bulk: Windows generates them through Event Tracing for Windows (ETW), and analytical events account for the majority of DNS events a server produces. Sending them unfiltered to a SIEM or XDR platform would have overwhelmed resources and driven up costs.
Volume was only part of the problem. The logs also needed parsing and enrichment before they were useful for detection and investigation. The company needed a way to separate the valuable signals from background noise, standardize the data format, and deliver it securely from hundreds of distributed systems — without hurting performance or compliance posture.

The Solution
The company chose NXLog Platform and deployed NXLog Agent across its DNS infrastructure.
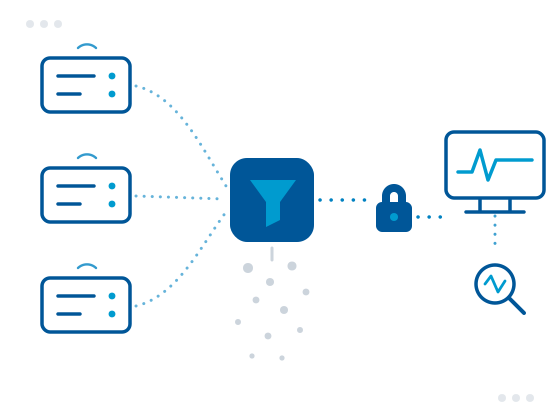
NXLog Agent's native ETW support captures DNS events directly from the Microsoft-Windows-DNSServer provider at the source, without writing them to disk first. Custom filtering rules excluded low-value queries and noise, refocusing collection on high-relevance events: unusual query types, NXDOMAIN responses, and patterns associated with known attack techniques.
Each event was parsed in depth to extract fields such as query names, query types, source IPs, and response codes. NXLog Agent normalized the data into structured JSON and enriched it with metadata, including the server hostname and event timestamp.
TLS encryption and certificate-based authentication secured delivery into Palo Alto Networks Cortex XSIAM, while disk and memory buffering with flow control kept data moving during network interruptions. Event data was collected in a consistent, verifiable form that supports audit and forensic review across the organization.
Why it Worked

Native ETW collection straight from the Windows DNS Server provider

Filtering at the source, before data reaches the SIEM

Structured JSON, enriched with hostname and timestamp

TLS encryption, certificate-based authentication, and buffered delivery
Results
With NXLog Platform, the organization gained a real-time view of security-critical DNS communications across its estate — without flooding its SIEM.
Filtering at the edge reduced ingestion costs while preserving the signal needed for threat detection. Analysts can now investigate DNS-based threats that were previously hidden in noise, using data the team could not practically collect before.
Compliance posture improved through consistent, encrypted, and traceable log collection across hundreds of distributed systems.

Unified DNS visibility
One real-time view of DNS activity across the Windows DNS estate
Lower SIEM ingestion
Low-value queries dropped at the source, before they reach the platform
Stronger threat detection
DNS-based threats surfaced from data that was previously unusable
Auditable, encrypted logs
Consistent, encrypted, traceable collection supporting compliance
About the customer
The customer is a major North American energy company that develops and operates critical energy infrastructure across Canada, the United States, and Mexico. Its business spans natural gas pipelines, liquid pipelines, and power generation.
Follow us


© Copyright NXLog Ltd.