
Axoflow alternative built for security teams
A pipeline is only as strong as what it collects.
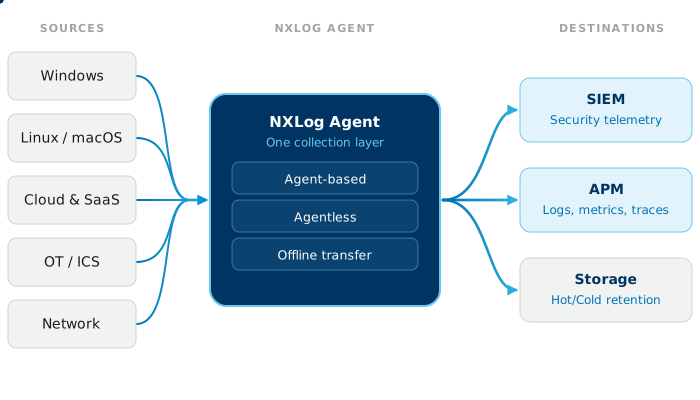
Axoflow curates the data your agents send it. NXLog Platform gives you the agents too. Collect security telemetry from Windows, Linux, macOS, and legacy Unix endpoints, process it at the source, and deliver it to any SIEM — with fleet management and storage built in.
Fortune 500 companies trust NXLog


Axoflow vs. NXLog Platform at a glance
Walk through NXLog Platform at your own pace — agent management, storage, and search included
Why teams choose NXLog Platform

One agent for every endpoint you own
NXLog Agent runs on Windows, Linux, macOS, FreeBSD, AIX, and Solaris, across x86, ARM, POWER, and SPARC hardware. Axoflow ships edge agents for two operating systems. Your fleet is bigger than that — your collection layer should cover it.

Windows telemetry beyond the Event Log
Axoflow's Windows agent collects files, Event Log, and ETW. NXLog Agent adds file integrity monitoring, Registry monitoring, packet capture, and native DNS and DHCP parsing — the endpoint signals your detection rules need, all from one lightweight agent.

Encrypted from the first hop
Axoflow's documentation states its agent-to-router transport currently runs without TLS or authentication. NXLog Agent encrypts data in transit with TLS/SSL, signs records with HMAC integrity checks, and can encrypt logs at rest — protection along the full path.

Configuration your auditors can read
Every NXLog pipeline is explicit configuration: versionable, reviewable, and testable before rollout. When a vendor's classifier updates itself, your pipeline changes without a change ticket. With NXLog, you decide what each agent collects, drops, and forwards.

Cut volume before it leaves the host
NXLog Agent filters, trims, and rewrites events at the point of collection, so noise never reaches your network or your SIEM bill. Source-based licensing means reduction costs you nothing — and incident-time volume spikes cost nothing extra.

Published pricing. Free to start.
NXLog Platform lists its prices: $5.58 per source per month at 100 sources, a free plan for up to 10 sources, and a 30-day trial with no credit card. You learn the cost without booking a call.
Not sure where to start? We're happy to map out what collection, routing, and retention would look like on NXLog Platform
Value by Team

Detection engineers
Your rules are only as good as the telemetry behind them. NXLog Agent delivers Event Log data with query-level filtering, ETW providers, file integrity and Registry changes, and DNS activity in structured form — ready for Splunk, Microsoft Sentinel, Google SecOps, or any SIEM you run.

Security architects
AIX in the datacenter, macOS on executive laptops, Solaris behind that one application nobody retires. NXLog covers them with the same agent and the same explicit configuration you can put through change control — and encrypts every hop in between.

SIEM budget owners
Ingestion pricing punishes visibility. NXLog trims noise at the endpoint before it crosses the network, and source-based licensing keeps your NXLog cost flat whether a host sends one event or one million. More filtering means direct SIEM savings.

IT teams consolidating agents
Running a forwarder here, a shipper there, and a collector for that one tool? NXLog Agent replaces the sprawl: files, syslog, Windows, cloud services, and databases through one enrolled, centrally managed agent with 120+ built-in integrations.
What you get with NXLog Platform
NXLog Agent: one collector, six operating systems
Deploy the same lightweight agent on Windows, Linux, macOS, FreeBSD, AIX, and Solaris — on x86, ARM, IBM POWER, and SPARC hardware. Enroll each agent to NXLog Platform for central configuration, monitoring, and updates. One codebase, one configuration language, one place to manage the whole fleet.
Windows depth that pipelines can't reach
Collect the Event Log with fine-grained queries, subscribe to ETW providers, watch files and Registry keys for changes, capture network traffic passively, and parse Microsoft DNS and DHCP logs natively. Prefer agentless? NXLog receives events forwarded over Windows Event Forwarding, too.
macOS and legacy Unix, first-party
NXLog Agent reads the macOS Unified Logging System and Apple Endpoint Security framework, Linux Audit, BSM auditing on Solaris and FreeBSD, and AIX kernel audit logs. If it runs in your estate, you can collect from it — without waiting for a third-party receiver to exist.
Processing at the point of collection
NXLog's configuration language filters, rewrites, enriches, correlates, and de-duplicates events on the agent itself. Drop the noise before it leaves the host, mask sensitive fields early, and convert formats — syslog, JSON, CSV, XML, CEF, LEEF — wherever it makes sense in the route.
Fleet management and storage included
NXLog Platform enrolls agents over a secured channel, pushes versioned configurations, monitors agent health, and stores logs with built-in search. Deploy it as your own instance and keep management and data under your control.
OpenTelemetry in both directions
NXLog Agent receives and sends OTLP over gRPC and HTTP — logs, metrics, and traces. Ready-made solution packs move Windows, macOS, Linux, and syslog data to OpenTelemetry backends, Splunk, Microsoft Sentinel, and Google SecOps in a few configuration steps.
Try NXLog Platform for free
FAQs
The two products overlap: both collect, process, route, and store security data centrally. The difference is where they start. Axoflow focuses on automatically curating data that agents and appliances send it. NXLog Platform starts at the endpoint, with first-party agents for six operating systems, then adds processing, delivery, management, and storage. If collection coverage is your gap, NXLog closes it directly.
Yes. NXLog Agent sends over syslog, OTLP (gRPC and HTTP), Kafka, HTTP(S), and more, so it can deliver to third-party routers and collectors — including syslog-ng-based tiers — while you evaluate. You don't need to rip anything out to start.
Yes — by filtering and trimming at the agent, before data crosses the network. The Port of Auckland's head of digital technology credits NXLog's filtering with letting the team “ingest only valuable events,” cutting spend on event volume. And because NXLog licenses by source, not gigabytes, reducing data never raises your NXLog bill.
If your telemetry is Kubernetes-first and your endpoints are already covered, Axoflow's cloud-native tooling is strong — see the section above. NXLog Agent runs on Linux hosts and in containers, but our depth is the endpoint estate: Windows, macOS, and legacy Unix. Choose by where your visibility gap is.
By source, with prices published on our plans page: from $12.12 per source per month at 11 sources down to $5.58 at 100, with volume discounts beyond that. The free plan covers up to 10 sources with no feature limits, and the 30-day Premium trial needs no credit card.
Axoflow, AxoRouter, AxoSyslog, Axolet, and AxoConsole are trademarks of Axoflow Inc. syslog-ng is a trademark of One Identity LLC. All other product names, logos, and brands are property of their respective owners and are used for identification purposes only. This comparison is based on publicly available documentation and pricing pages as of September 8, 2026
Follow us


© Copyright NXLog Ltd.