
A top automotive financial services company strengthened cybersecurity and achieved compliance with one unified log pipeline
With NXLog Platform, the company replaced an obsolete log collection solution, unified collection across its global multi-vendor infrastructure — including air-gapped nodes — and met SEC, SOX, PCI DSS, and GLBA requirements for log retention and analysis.

Business Demand
Improve security posture and meet SEC, SOX, PCI DSS, and GLBA requirements, plus national and corporate regulations for log retention and analysis.
Key Challenges
Replace an obsolete log collection solution with a secure, time- and cost-effective pipeline across multi-vendor infrastructure, including air-gapped nodes.
Results
A unified, autonomous log collection pipeline, simplified event source integration, broader collection coverage, and compliance achieved.
We are very pleased working with NXLog and really appreciate all the advanced features of the product. We were looking for a lightweight log collection tool, that allows to flexibly filter and transform events, while keeping it easy to deploy agents across Microsoft infrastructure. We considered NXLog as the most versatile product that completely fulfill all the needs for us.
— CISO, Automotive Financial Services Company

The Challenge
Financial services companies operate under regulations such as GDPR, PCI DSS, SOX, and GLBA that mandate safeguarding infrastructure and customer financial data. Successful attacks on financial firms are lucrative for cybercriminals, so a detailed, up-to-date view of all network activity is essential to defend against them.
The company’s existing log collection solution had become obsolete, ineffective, and difficult to manage. A solid log management process needed a reliable pipeline across the entire network infrastructure — including air-gapped nodes.
The main challenge was the variety of target systems from different vendors, each with its own logging capabilities and technologies. To solve it, the company set out to implement a vendor-agnostic log collection pipeline that allows fast, easy integration of old and new network endpoints and applications.

The Solution
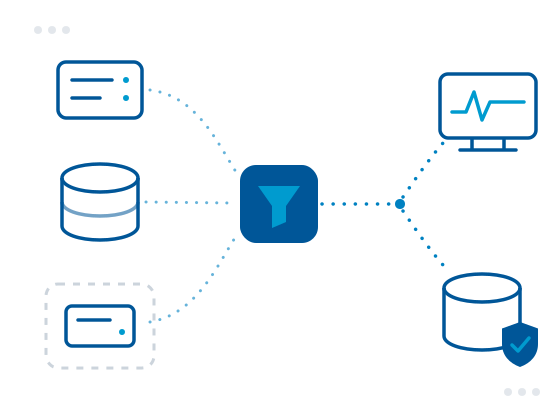
The company chose NXLog Platform to build a unified, autonomous log collection pipeline for event retention and ongoing threat analysis.
The NXLog Agent collects from a wide range of log sources, including Windows event logs, and can process volumes of more than 100,000 events per second. It supports all standard network protocols, collects logs from files and databases, and handles common log formats out of the box, with more than 120 built-in extensions for collection, processing, and routing. Deployment across the company’s Microsoft Windows infrastructure was quick: agents roll out via Windows Group Policy with a signed package.
Log collection is never a one-time task. Agents and forwarders need ongoing monitoring and management while new endpoints join the pipeline. Rich data filtering and transformation were also key requirements: pick only the events that matter for a specific job — such as security — skip high-volume diagnostics, and reshape messages to match the central store, whether that is a SIEM or an APM system.
The NXLog Agent performs advanced processing on log messages, including rewriting, correlation, alerting, pattern matching, scheduling, and log file rotation. It prioritizes specific messages and buffers data on disk or in memory to work around input latency and network congestion. After processing, it stores or forwards events in many supported formats, including to SIEM solutions such as Microsoft Sentinel, Google Security Operations (formerly Google Chronicle), OpenText ArcSight, and IBM QRadar.
The new unified log collection pipeline now helps the company meet both corporate and national regulations.
Why it Worked

Lightweight agent, deployed across Windows infrastructure via Group Policy

Rich event filtering and transformation before data leaves the source

Vendor-agnostic forwarding to SIEM and APM destinations

Disk and memory buffering for reliable delivery across the pipeline
Results
A unified and autonomous log collection pipeline now runs across the company’s global infrastructure. Ongoing event source integration is simpler: new endpoints and applications join the pipeline without vendor-specific rework.
Broader log collection coverage improved the company’s security posture, giving engineering and security teams a detailed, current view of network activity for threat analysis and faster resolution of production and security issues. Filtering out extraneous data at the source also cut data retention expenses.
Most importantly, the company achieved compliance: the pipeline meets SEC, SOX, PCI DSS, and GLBA requirements, plus national and corporate regulations for log retention and analysis.

Unified pipeline
One autonomous log collection pipeline across the entire infrastructure
Simplified integration
New event sources join the pipeline quickly, old and new alike
Stronger security posture
Broader collection coverage and a current view of network activity
Compliance achieved
SEC, SOX, PCI DSS, and GLBA, plus national and corporate retention rules
About the customer
The customer is a business division of one of the world’s top-tier automotive groups, with thousands of employees working at dozens of branches across the globe. Its services span automotive financial services, direct banking, financing, leasing and insurance, fleet management, and payment and rental solutions.
Follow us


© Copyright NXLog Ltd.